Turning Noisy Physical Signals into Reliable Cryptographic Keys
Your Fingerprint Never Looks Exactly the Same Twice
Think about what happens when you place your finger on a fingerprint sensor. The angle of your finger, how firmly you press, and even the humidity that day can slightly change the image captured by the sensor. The fingerprint you enrolled yesterday and the one you scan today are almost never identical down to every pixel.
Yet we still use fingerprints to unlock devices and authorize payments. That works because biometric systems are not designed to look for a perfectly identical image. They are designed to determine whether two scans are similar enough to belong to the same person.
A PUF, or Physically Unclonable Function, faces a fundamentally similar challenge. A PUF derives a unique value from microscopic variations that naturally occur during semiconductor manufacturing. These physical variations differ from chip to chip and are extremely difficult to predict or reproduce. The challenge is that, much like a fingerprint scan, a PUF response may not always be perfectly identical every time it is measured.
Cryptographic keys, however, leave no room for "close enough." If even a single bit changes, the result is an entirely different key. So how can a physical signal that may naturally fluctuate be turned into a cryptographic key that must remain exactly the same every time?
A PUF Is Fundamentally a Measurement — and Measurements Can Vary
A PUF response is not simply a number calculated by software. It is derived from a physical measurement. PUFs exploit tiny manufacturing variations such as differences in transistor threshold voltage, resistance, timing, or material dimensions. These variations arise naturally during semiconductor fabrication and cannot be precisely predicted or reproduced in advance by either the chip designer or the manufacturer. That unpredictability is exactly what gives a PUF its unclonable characteristics.
But as with any physical measurement, the resulting signal can be affected by its environment. Changes in temperature alter the electrical characteristics of semiconductor devices. Variations in supply voltage can shift measurement thresholds. Over time, device aging can also gradually change electrical behavior. As a result, even when the same location on the same chip is measured repeatedly, some bits may occasionally flip between readings.
The rate at which those bits change across repeated measurements is commonly referred to as the Bit Error Rate, or BER. Depending on the type of PUF, implementation, and cell-selection methodology, reported BERs can vary significantly and may reach double-digit percentages in some implementations. The international standard ISO/IEC 20897-1 defines security requirements and output characteristics for physically unclonable functions and identifies reliability as one of the fundamental considerations in PUF design.
This is where different PUF architectures begin to diverge significantly. The degree of variation depends heavily on which physical phenomenon is being used as the entropy source. Among the key security properties expected of a PUF are Randomness, Uniqueness, Unclonability, and Steadiness. While Randomness, Uniqueness, and physical or mathematical unclonability focus largely on how unpredictable and distinguishable a PUF is, Steadiness asks almost the opposite question: how consistently can the same value be reproduced over time and across changing operating conditions? That makes Steadiness one of the more difficult trade-offs in PUF design. A PUF must be unpredictable across different devices, yet highly predictable when the same device is measured again. We will return to how different PUF architectures address this trade-off later.
One of the major advantages of PUF technology is that a key does not necessarily need to be permanently stored. Instead, it can be reconstructed from the device's physical characteristics whenever it is needed. But that advantage comes with a demanding requirement: every reconstruction must produce exactly the same cryptographic value. Solving that problem is what makes it possible to use PUFs in real cryptographic systems.
Three Ways to Turn a Noisy Signal into a Reliable Value
Over time, several approaches have been developed to derive consistent values from noisy physical PUF responses. These techniques are not necessarily mutually exclusive. In real-world implementations, multiple approaches may be combined.
Majority Voting — Simple, but Not Always Enough
The most straightforward approach is to measure the same bit multiple times and determine its value through majority voting. For example, if a bit is measured ten times and returns a 1 seven times, the system may classify that bit as 1. The advantage is simplicity. Majority voting can be implemented without significant additional circuitry or complex error-correction logic. However, it does not eliminate the underlying cause of instability, such as temperature or voltage variation. It merely reduces the probability of an incorrect reading. As a result, it becomes less effective when the underlying PUF has a relatively high error rate. Repeated measurements also introduce trade-offs in response time and power consumption.
Filtering Out Unreliable Bits — Dark-Bit Masking
A second approach is to identify unstable bits in advance and simply avoid using them. During manufacturing or enrollment, each PUF cell can be measured repeatedly to determine how reliably it reproduces the same value. Bits that show poor stability — sometimes referred to as dark bits — are recorded and excluded from subsequent key generation. By using only highly stable cells, the effective BER of the selected PUF response can be reduced substantially. But this approach introduces other design considerations. The system must securely manage information identifying which bits should be excluded. And because fewer PUF cells remain usable, the design may require a larger number of raw cells to generate a cryptographic key of the desired length.
Fuzzy Extractors and Helper Data — The Conventional Approach
A third approach, and one widely studied and implemented across academia and industry, is the Fuzzy Extractor. The theoretical foundation for fuzzy extractors was established by Dodis, Ostrovsky, Reyzin, and Smith, first presented at EUROCRYPT in 2004 and later published in the SIAM Journal on Computing in 2008.
The basic idea is straightforward. During the initial enrollment stage, the raw PUF response is measured. The system then generates auxiliary information using an Error-Correcting Code (ECC). This auxiliary information, commonly called Helper Data, is stored for later use. When the key is needed again, the PUF is re-measured. Even if the newly measured response differs slightly from the original because of noise, the stored Helper Data allows the system to correct those errors and reconstruct the original value.
There is one critical design principle here: Helper Data should not reveal the original PUF response itself. When designed properly, Helper Data can therefore be stored in non-volatile memory without requiring the same level of secrecy as the cryptographic key itself.
This architecture also has another useful property. Small variations that fall within the correction capability of the ECC can be corrected. But larger physical changes — potentially including damage caused by tampering — may exceed the correction threshold and cause reconstruction to fail. In some designs, that failure itself can serve as an indication that something abnormal has occurred.
| Approach | Core Principle | Advantages | Limitations |
| Majority Voting | Measure the same bit repeatedly and determine its value statistically | Simple implementation and relatively low circuit overhead | Limited effectiveness at high BER; additional latency and power consumption |
| Dark-Bit Masking | Identify and exclude unstable bits during enrollment or testing | Can significantly reduce BER among selected bits | Requires mask management and a larger pool of raw PUF cells |
| Fuzzy Extractor + ECC / Helper Data | Correct noisy PUF responses and reconstruct the original value using error-correcting codes | Well-established theoretical foundation; Helper Data can typically be stored openly when properly designed | Adds ECC design and implementation complexity; cannot correct errors beyond the configured correction capability |
The references at the end of this article provide additional background on the theory and implementation of these approaches. Because the performance and efficiency of individual error-correction schemes can vary significantly depending on the specific PUF architecture and hardware implementation, it is generally more useful to evaluate BER figures together with their underlying test conditions rather than compare isolated numbers.
Stability Is Reliability in a Real System
The importance of PUF stability becomes much clearer when we consider where these devices are actually deployed. Automotive electronics, industrial IoT gateways, outdoor telecommunications equipment, and other embedded systems often operate across much wider temperature ranges and voltage conditions than devices tested in a laboratory.
In these environments, a single failure to reconstruct a PUF-derived key can mean much more than a software bug. If a device cannot reproduce the key required to authenticate itself, establish a secure connection, or verify trusted code, the device may effectively lose its ability to prove that it can be trusted. The entire chain of trust can stop at that point. That is why the stabilization and reproducibility of a PUF response can be just as important as the cryptographic algorithm that ultimately uses the generated key.
Why Steadiness Matters for VIA PUF™
This is also why ICTK considers Steadiness one of the defining strengths of VIA PUF™. VIA PUF™ derives its value from whether physical conductive connections are formed during semiconductor fabrication. This gives it a fundamentally different starting point from PUF architectures that depend on continuously measuring small analog differences in active semiconductor devices. Rather than repeatedly interpreting subtle electrical variations, VIA PUF™ uses the physical connectivity state of a via itself as the binary source for 0s and 1s.
🔗 Learn More About VIA PUF™
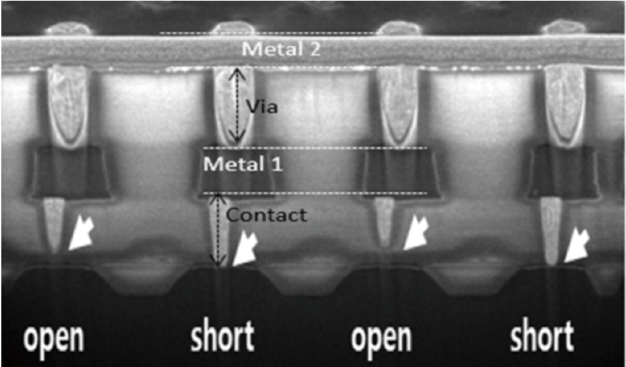
At the core of VIA PUF™ is a simple distinction. It does not determine 0 and 1 by repeatedly measuring small electrical differences during operation. Instead, it uses the physical connected or non-connected state of vias formed during manufacturing as its entropy source. Because these physical states are designed to remain stable across environmental changes such as temperature, voltage variation, and aging, VIA PUF™ can reproduce the same values without relying on conventional Error-Correcting Codes or Helper Data for key reconstruction.
In other words, VIA PUF™ starts with a highly stable physical state established during manufacturing. This architecture minimizes bit errors at the source rather than correcting them afterward. The result is a PUF architecture designed to reconstruct the same cryptographic key consistently across a wide operating temperature and voltage range and throughout long-term device operation.
In Summary
Because a PUF derives its response from physical characteristics, noise and variation are inherent challenges. The goal of PUF security design is therefore not simply to pretend that noise does not exist. It is to ensure that the same exact cryptographic value can be reconstructed every time despite that noise.
Majority voting, unstable-bit masking, and fuzzy extractors using ECC and Helper Data all take different approaches to solving the same fundamental problem: how do you derive a key that is as precise and reproducible as a stored cryptographic key from a physical fingerprint that was never stored as a key in the first place?
That question sits at the heart of practical PUF implementation. And the answer depends heavily on the physical architecture behind the PUF itself.
See How VIA PUF™ Works
Want to learn more about how VIA PUF™ reconstructs stable cryptographic keys from silicon?
☑️ Explore the VIA PUF™ Security IP
References
ISO/IEC 20897-1:2020 — Physically unclonable functions — Part 1: Security requirements
Dodis, Ostrovsky, Reyzin, Smith, "Fuzzy Extractors: How to Generate Strong Keys from Biometrics and Other Noisy Data," SIAM Journal on Computing, 2008
Delvaux, "Review of error correction for PUFs and evaluation on state-of-the-art FPGAs," Journal of Cryptographic Engineering, 2020


Turning Noisy Physical Signals into Reliable Cryptographic Keys
Your Fingerprint Never Looks Exactly the Same Twice
Think about what happens when you place your finger on a fingerprint sensor. The angle of your finger, how firmly you press, and even the humidity that day can slightly change the image captured by the sensor. The fingerprint you enrolled yesterday and the one you scan today are almost never identical down to every pixel.
Yet we still use fingerprints to unlock devices and authorize payments. That works because biometric systems are not designed to look for a perfectly identical image. They are designed to determine whether two scans are similar enough to belong to the same person.
A PUF, or Physically Unclonable Function, faces a fundamentally similar challenge. A PUF derives a unique value from microscopic variations that naturally occur during semiconductor manufacturing. These physical variations differ from chip to chip and are extremely difficult to predict or reproduce. The challenge is that, much like a fingerprint scan, a PUF response may not always be perfectly identical every time it is measured.
Cryptographic keys, however, leave no room for "close enough." If even a single bit changes, the result is an entirely different key. So how can a physical signal that may naturally fluctuate be turned into a cryptographic key that must remain exactly the same every time?
A PUF Is Fundamentally a Measurement — and Measurements Can Vary
A PUF response is not simply a number calculated by software. It is derived from a physical measurement. PUFs exploit tiny manufacturing variations such as differences in transistor threshold voltage, resistance, timing, or material dimensions. These variations arise naturally during semiconductor fabrication and cannot be precisely predicted or reproduced in advance by either the chip designer or the manufacturer. That unpredictability is exactly what gives a PUF its unclonable characteristics.
But as with any physical measurement, the resulting signal can be affected by its environment. Changes in temperature alter the electrical characteristics of semiconductor devices. Variations in supply voltage can shift measurement thresholds. Over time, device aging can also gradually change electrical behavior. As a result, even when the same location on the same chip is measured repeatedly, some bits may occasionally flip between readings.
The rate at which those bits change across repeated measurements is commonly referred to as the Bit Error Rate, or BER. Depending on the type of PUF, implementation, and cell-selection methodology, reported BERs can vary significantly and may reach double-digit percentages in some implementations. The international standard ISO/IEC 20897-1 defines security requirements and output characteristics for physically unclonable functions and identifies reliability as one of the fundamental considerations in PUF design.
This is where different PUF architectures begin to diverge significantly. The degree of variation depends heavily on which physical phenomenon is being used as the entropy source. Among the key security properties expected of a PUF are Randomness, Uniqueness, Unclonability, and Steadiness. While Randomness, Uniqueness, and physical or mathematical unclonability focus largely on how unpredictable and distinguishable a PUF is, Steadiness asks almost the opposite question: how consistently can the same value be reproduced over time and across changing operating conditions? That makes Steadiness one of the more difficult trade-offs in PUF design. A PUF must be unpredictable across different devices, yet highly predictable when the same device is measured again. We will return to how different PUF architectures address this trade-off later.
One of the major advantages of PUF technology is that a key does not necessarily need to be permanently stored. Instead, it can be reconstructed from the device's physical characteristics whenever it is needed. But that advantage comes with a demanding requirement: every reconstruction must produce exactly the same cryptographic value. Solving that problem is what makes it possible to use PUFs in real cryptographic systems.
Three Ways to Turn a Noisy Signal into a Reliable Value
Over time, several approaches have been developed to derive consistent values from noisy physical PUF responses. These techniques are not necessarily mutually exclusive. In real-world implementations, multiple approaches may be combined.
Majority Voting — Simple, but Not Always Enough
The most straightforward approach is to measure the same bit multiple times and determine its value through majority voting. For example, if a bit is measured ten times and returns a 1 seven times, the system may classify that bit as 1. The advantage is simplicity. Majority voting can be implemented without significant additional circuitry or complex error-correction logic. However, it does not eliminate the underlying cause of instability, such as temperature or voltage variation. It merely reduces the probability of an incorrect reading. As a result, it becomes less effective when the underlying PUF has a relatively high error rate. Repeated measurements also introduce trade-offs in response time and power consumption.
Filtering Out Unreliable Bits — Dark-Bit Masking
A second approach is to identify unstable bits in advance and simply avoid using them. During manufacturing or enrollment, each PUF cell can be measured repeatedly to determine how reliably it reproduces the same value. Bits that show poor stability — sometimes referred to as dark bits — are recorded and excluded from subsequent key generation. By using only highly stable cells, the effective BER of the selected PUF response can be reduced substantially. But this approach introduces other design considerations. The system must securely manage information identifying which bits should be excluded. And because fewer PUF cells remain usable, the design may require a larger number of raw cells to generate a cryptographic key of the desired length.
Fuzzy Extractors and Helper Data — The Conventional Approach
A third approach, and one widely studied and implemented across academia and industry, is the Fuzzy Extractor. The theoretical foundation for fuzzy extractors was established by Dodis, Ostrovsky, Reyzin, and Smith, first presented at EUROCRYPT in 2004 and later published in the SIAM Journal on Computing in 2008.
The basic idea is straightforward. During the initial enrollment stage, the raw PUF response is measured. The system then generates auxiliary information using an Error-Correcting Code (ECC). This auxiliary information, commonly called Helper Data, is stored for later use. When the key is needed again, the PUF is re-measured. Even if the newly measured response differs slightly from the original because of noise, the stored Helper Data allows the system to correct those errors and reconstruct the original value.
There is one critical design principle here: Helper Data should not reveal the original PUF response itself. When designed properly, Helper Data can therefore be stored in non-volatile memory without requiring the same level of secrecy as the cryptographic key itself.
This architecture also has another useful property. Small variations that fall within the correction capability of the ECC can be corrected. But larger physical changes — potentially including damage caused by tampering — may exceed the correction threshold and cause reconstruction to fail. In some designs, that failure itself can serve as an indication that something abnormal has occurred.
The references at the end of this article provide additional background on the theory and implementation of these approaches. Because the performance and efficiency of individual error-correction schemes can vary significantly depending on the specific PUF architecture and hardware implementation, it is generally more useful to evaluate BER figures together with their underlying test conditions rather than compare isolated numbers.
Stability Is Reliability in a Real System
The importance of PUF stability becomes much clearer when we consider where these devices are actually deployed. Automotive electronics, industrial IoT gateways, outdoor telecommunications equipment, and other embedded systems often operate across much wider temperature ranges and voltage conditions than devices tested in a laboratory.
In these environments, a single failure to reconstruct a PUF-derived key can mean much more than a software bug. If a device cannot reproduce the key required to authenticate itself, establish a secure connection, or verify trusted code, the device may effectively lose its ability to prove that it can be trusted. The entire chain of trust can stop at that point. That is why the stabilization and reproducibility of a PUF response can be just as important as the cryptographic algorithm that ultimately uses the generated key.
Why Steadiness Matters for VIA PUF™
This is also why ICTK considers Steadiness one of the defining strengths of VIA PUF™. VIA PUF™ derives its value from whether physical conductive connections are formed during semiconductor fabrication. This gives it a fundamentally different starting point from PUF architectures that depend on continuously measuring small analog differences in active semiconductor devices. Rather than repeatedly interpreting subtle electrical variations, VIA PUF™ uses the physical connectivity state of a via itself as the binary source for 0s and 1s.
🔗 Learn More About VIA PUF™
At the core of VIA PUF™ is a simple distinction. It does not determine 0 and 1 by repeatedly measuring small electrical differences during operation. Instead, it uses the physical connected or non-connected state of vias formed during manufacturing as its entropy source. Because these physical states are designed to remain stable across environmental changes such as temperature, voltage variation, and aging, VIA PUF™ can reproduce the same values without relying on conventional Error-Correcting Codes or Helper Data for key reconstruction.
In other words, VIA PUF™ starts with a highly stable physical state established during manufacturing. This architecture minimizes bit errors at the source rather than correcting them afterward. The result is a PUF architecture designed to reconstruct the same cryptographic key consistently across a wide operating temperature and voltage range and throughout long-term device operation.
In Summary
Because a PUF derives its response from physical characteristics, noise and variation are inherent challenges. The goal of PUF security design is therefore not simply to pretend that noise does not exist. It is to ensure that the same exact cryptographic value can be reconstructed every time despite that noise.
Majority voting, unstable-bit masking, and fuzzy extractors using ECC and Helper Data all take different approaches to solving the same fundamental problem: how do you derive a key that is as precise and reproducible as a stored cryptographic key from a physical fingerprint that was never stored as a key in the first place?
That question sits at the heart of practical PUF implementation. And the answer depends heavily on the physical architecture behind the PUF itself.
See How VIA PUF™ Works
Want to learn more about how VIA PUF™ reconstructs stable cryptographic keys from silicon?
☑️ Explore the VIA PUF™ Security IP
References
ISO/IEC 20897-1:2020 — Physically unclonable functions — Part 1: Security requirements
Dodis, Ostrovsky, Reyzin, Smith, "Fuzzy Extractors: How to Generate Strong Keys from Biometrics and Other Noisy Data," SIAM Journal on Computing, 2008
Delvaux, "Review of error correction for PUFs and evaluation on state-of-the-art FPGAs," Journal of Cryptographic Engineering, 2020