The best lock in the world doesn't help once someone walks off with the whole safe
Firewalls, encryption, access control — most security conversations assume the attacker is coming in over the network. But what if someone gets their hands on the physical device, pries the case open, and starts probing the chip itself? For payment terminals, smart cards, and IoT gateways — anything that can end up in a stranger's hands — that's not a hypothetical. It's a real attack surface. The technologies and design principles built to withstand that kind of attack fall under one umbrella: anti-tamper. Here are the 9 questions people ask most.
Q1. What is anti-tamper technology?
Anti-tamper refers to the technologies and design principles that prevent — or detect and respond to — attempts to physically open or manipulate hardware. NIST's security control catalog, SP 800-53, defines this under control SR-9 ("Tamper Resistance and Detection") as requiring "anti-tamper technologies, tools, and techniques" to protect systems and components against threats like reverse engineering, unauthorized modification, and substitution.
It's not one specific part or component — it's an umbrella term covering a chain of design principles: resistance, evidence, detection, and response. We break that chain down in Q3.
Q2. Why would anyone bother physically attacking a chip?
Usually to steal a cryptographic key or credential stored inside, bypass authentication logic to build a counterfeit, or quietly alter how the device behaves. A system that's unbreakable over the network suddenly has a completely different attack surface the moment someone gets physical access to the hardware.
That's why physical attacks are treated as a real, present threat — not a theoretical one — for products like point-of-sale terminals, smart cards, IoT gateways, and metering equipment, where the device itself can end up in an attacker's hands during use or even in transit. Even brief physical access during shipping or storage is enough to tamper with a device, which is exactly why anti-tamper design matters for supply chain security too.
Q3. What's the difference between tamper resistance and tamper detection?
Tamper resistance makes physical access to the internals difficult and expensive in the first place. Tamper detection recognizes an access or manipulation attempt as it's happening. The industry typically breaks this into four stages:
- Tamper resistance: Hardened potting compounds, buried internal wiring layers, and similar techniques make physical access itself difficult.
- Tamper evidence: Opening the enclosure leaves visible signs — a broken seal, damaged casing — that prove tampering happened after the fact, even though it didn't stop the attack.
- Tamper detection: Mesh wiring, and light, temperature, or voltage sensors flag an intrusion attempt in real time.
- Tamper response: The moment tampering is detected, the device erases stored keys (zeroization) or disables itself entirely.
Q4. How does anti-tamper relate to PUF technology?
A PUF (Physically Unclonable Function) generates a key on the fly from the random physical variation baked into a chip during manufacturing, instead of storing that key anywhere. Because there's no stored key to find, an invasive attacker who opens the chip and reads its memory has nothing to steal — which gives PUF a natural tamper-resistant quality.
That said, PUF isn't a substitute for anti-tamper as a whole. Real products typically pair PUF with other physical protection layers — potting compounds, sensor meshes, secure floor-planning. PUF is the "leave nothing to steal" approach; the rest of anti-tamper design is about making the attempt itself hard or catching it in the act. The two complement each other rather than compete.
Q5. What kinds of attacks does anti-tamper actually stop?
Physical attacks generally fall into three categories — non-invasive, semi-invasive, and invasive — and anti-tamper design responds to each one differently.
- Non-invasive attacks: Side-channel attacks are the classic example — measuring external signals like power draw or electromagnetic emissions to infer internal values, without ever opening the chip.
- Semi-invasive attacks: Fault injection falls here — partially exposing the chip's surface and using lasers, UV light, or electromagnetic pulses to force a malfunction.
- Invasive attacks: Fully removing the package and using probing equipment to read or manipulate the internal wiring directly — the most expensive and most thorough attack type.
Anti-tamper design typically layers countermeasures — power-noise injection, wiring meshes, encapsulation — matched to each attack category to cover the full range.
Q6. Are there any standards or certifications for anti-tamper?
Yes. FIPS 140-3, the cryptographic module validation standard maintained by NIST, is the most widely cited one. It defines physical security requirements across four levels:
- Level 1: No specific physical security requirements.
- Level 2: Requires tamper evidence — visible signs if the case is opened.
- Level 3: Adds tamper resistance and detection, plus environmental failure protection/testing (EFP/EFT) against abnormal voltage or temperature.
- Level 4: Requires real-time response to any physical access attempt (tamper-active), including immediate data erasure the moment tampering is detected.
Procurement requirements in finance, government, and defense frequently specify a minimum FIPS 140-3 level.
Q7. Can't software security alone stop tampering?
No, it can't. Software security assumes the system boots and runs the way it's supposed to — but a physical tamper attack breaks that exact assumption by compromising the integrity of the hardware itself.
Reading a key directly out of memory by opening the chip, for instance, isn't something any OS patch or application-layer security update can stop. That's exactly why a hardware root of trust and anti-tamper design have to exist as a layer separate from software security — no software update can add them after the fact.
Q8. Which industries or products need anti-tamper the most?
It matters most for products that operate for long periods within physical reach of users — or potential attackers: payment and financial terminals (POS systems, ATMs, smart cards), defense and aerospace equipment, medical devices, industrial IoT and metering equipment, and automotive ECUs.
In these industries, a single compromised or cloned device can translate directly into financial loss or a large-scale data breach, which is why anti-tamper requirements are typically written into the design from day one rather than added later.
Q9. How Is Anti-Tamper Different from Physical Security and Cybersecurity?
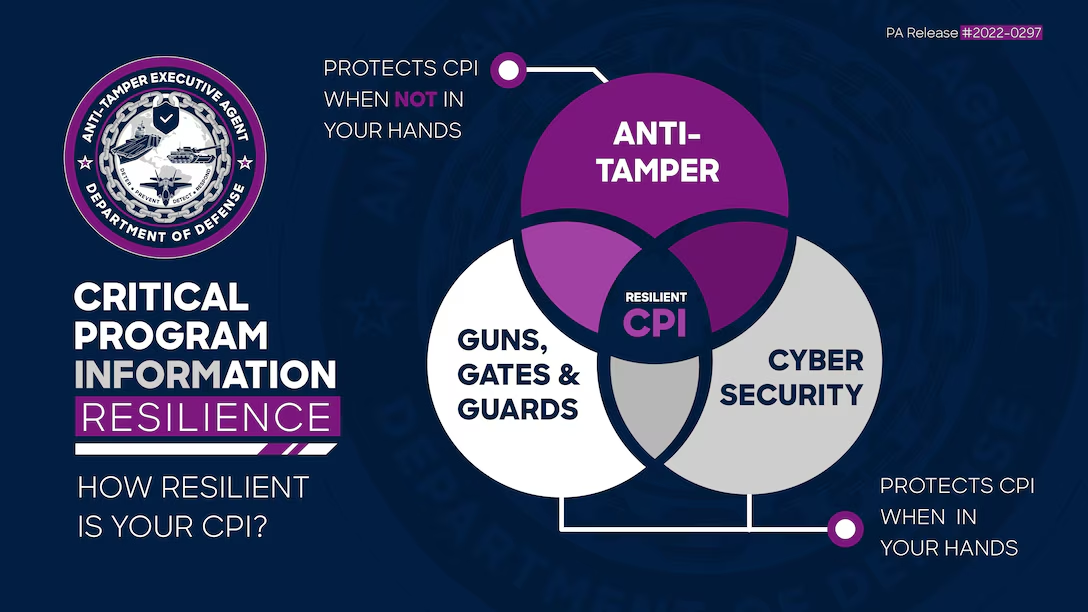
The U.S. Department of Defense Anti-Tamper Executive Agent distinguishes anti-tamper, physical security, and cybersecurity by when each protects Critical Program Information (CPI). Guns, Gates & Guards and cybersecurity protect CPI while equipment remains under our control, such as during operation or storage. Anti-tamper, by contrast, serves as the final line of defense once equipment leaves our control—whether through export, loss on the battlefield, end-of-life disposal, or other circumstances.
img source: https://at.dod.mil/What-Is-Anti-Tamper/
The agency’s “CPI Resilience” diagram illustrates that truly resilient CPI is achieved only when anti-tamper, physical security, and cybersecurity overlap. In other words, anti-tamper does not replace physical or cybersecurity measures. It complements them by continuing to protect CPI when those measures can no longer provide effective protection.
References
See it in action
Anti-tamper comes down to two things working together: designing so there's nothing physical left to steal, and designing to catch someone trying anyway. If you're curious how ICTK's VIA PUF resists invasive attacks by never storing a key in the first place, reach out to our team.
☑️ Contact us


The best lock in the world doesn't help once someone walks off with the whole safe
Firewalls, encryption, access control — most security conversations assume the attacker is coming in over the network. But what if someone gets their hands on the physical device, pries the case open, and starts probing the chip itself? For payment terminals, smart cards, and IoT gateways — anything that can end up in a stranger's hands — that's not a hypothetical. It's a real attack surface. The technologies and design principles built to withstand that kind of attack fall under one umbrella: anti-tamper. Here are the 9 questions people ask most.
Q1. What is anti-tamper technology?
Anti-tamper refers to the technologies and design principles that prevent — or detect and respond to — attempts to physically open or manipulate hardware. NIST's security control catalog, SP 800-53, defines this under control SR-9 ("Tamper Resistance and Detection") as requiring "anti-tamper technologies, tools, and techniques" to protect systems and components against threats like reverse engineering, unauthorized modification, and substitution.
It's not one specific part or component — it's an umbrella term covering a chain of design principles: resistance, evidence, detection, and response. We break that chain down in Q3.
Q2. Why would anyone bother physically attacking a chip?
Usually to steal a cryptographic key or credential stored inside, bypass authentication logic to build a counterfeit, or quietly alter how the device behaves. A system that's unbreakable over the network suddenly has a completely different attack surface the moment someone gets physical access to the hardware.
That's why physical attacks are treated as a real, present threat — not a theoretical one — for products like point-of-sale terminals, smart cards, IoT gateways, and metering equipment, where the device itself can end up in an attacker's hands during use or even in transit. Even brief physical access during shipping or storage is enough to tamper with a device, which is exactly why anti-tamper design matters for supply chain security too.
Q3. What's the difference between tamper resistance and tamper detection?
Tamper resistance makes physical access to the internals difficult and expensive in the first place. Tamper detection recognizes an access or manipulation attempt as it's happening. The industry typically breaks this into four stages:
Q4. How does anti-tamper relate to PUF technology?
A PUF (Physically Unclonable Function) generates a key on the fly from the random physical variation baked into a chip during manufacturing, instead of storing that key anywhere. Because there's no stored key to find, an invasive attacker who opens the chip and reads its memory has nothing to steal — which gives PUF a natural tamper-resistant quality.
That said, PUF isn't a substitute for anti-tamper as a whole. Real products typically pair PUF with other physical protection layers — potting compounds, sensor meshes, secure floor-planning. PUF is the "leave nothing to steal" approach; the rest of anti-tamper design is about making the attempt itself hard or catching it in the act. The two complement each other rather than compete.
Q5. What kinds of attacks does anti-tamper actually stop?
Physical attacks generally fall into three categories — non-invasive, semi-invasive, and invasive — and anti-tamper design responds to each one differently.
Anti-tamper design typically layers countermeasures — power-noise injection, wiring meshes, encapsulation — matched to each attack category to cover the full range.
Q6. Are there any standards or certifications for anti-tamper?
Yes. FIPS 140-3, the cryptographic module validation standard maintained by NIST, is the most widely cited one. It defines physical security requirements across four levels:
Procurement requirements in finance, government, and defense frequently specify a minimum FIPS 140-3 level.
Q7. Can't software security alone stop tampering?
No, it can't. Software security assumes the system boots and runs the way it's supposed to — but a physical tamper attack breaks that exact assumption by compromising the integrity of the hardware itself.
Reading a key directly out of memory by opening the chip, for instance, isn't something any OS patch or application-layer security update can stop. That's exactly why a hardware root of trust and anti-tamper design have to exist as a layer separate from software security — no software update can add them after the fact.
Q8. Which industries or products need anti-tamper the most?
It matters most for products that operate for long periods within physical reach of users — or potential attackers: payment and financial terminals (POS systems, ATMs, smart cards), defense and aerospace equipment, medical devices, industrial IoT and metering equipment, and automotive ECUs.
In these industries, a single compromised or cloned device can translate directly into financial loss or a large-scale data breach, which is why anti-tamper requirements are typically written into the design from day one rather than added later.
Q9. How Is Anti-Tamper Different from Physical Security and Cybersecurity?
The U.S. Department of Defense Anti-Tamper Executive Agent distinguishes anti-tamper, physical security, and cybersecurity by when each protects Critical Program Information (CPI). Guns, Gates & Guards and cybersecurity protect CPI while equipment remains under our control, such as during operation or storage. Anti-tamper, by contrast, serves as the final line of defense once equipment leaves our control—whether through export, loss on the battlefield, end-of-life disposal, or other circumstances.
img source: https://at.dod.mil/What-Is-Anti-Tamper/
The agency’s “CPI Resilience” diagram illustrates that truly resilient CPI is achieved only when anti-tamper, physical security, and cybersecurity overlap. In other words, anti-tamper does not replace physical or cybersecurity measures. It complements them by continuing to protect CPI when those measures can no longer provide effective protection.
References
See it in action
Anti-tamper comes down to two things working together: designing so there's nothing physical left to steal, and designing to catch someone trying anyway. If you're curious how ICTK's VIA PUF resists invasive attacks by never storing a key in the first place, reach out to our team.
☑️ Contact us